

Compare the levels
Scan levels describe what a scan checks, not how severe a finding is. Findings have separate severity ratings, such as critical, high, medium, and low.
Level 1 is free. Level 2 requires a paid Replit plan. Level 3 has additional plan and project-access requirements.
Agent work in Levels 2 and 3 is subject to Agent usage billing.
If a scan level is unavailable, check your project’s access and the upgrade guidance in Security Center.
Level 1: Basic security checks
Level 1 runs free dependency and package checks. Use it to find known vulnerabilities in the libraries your app depends on.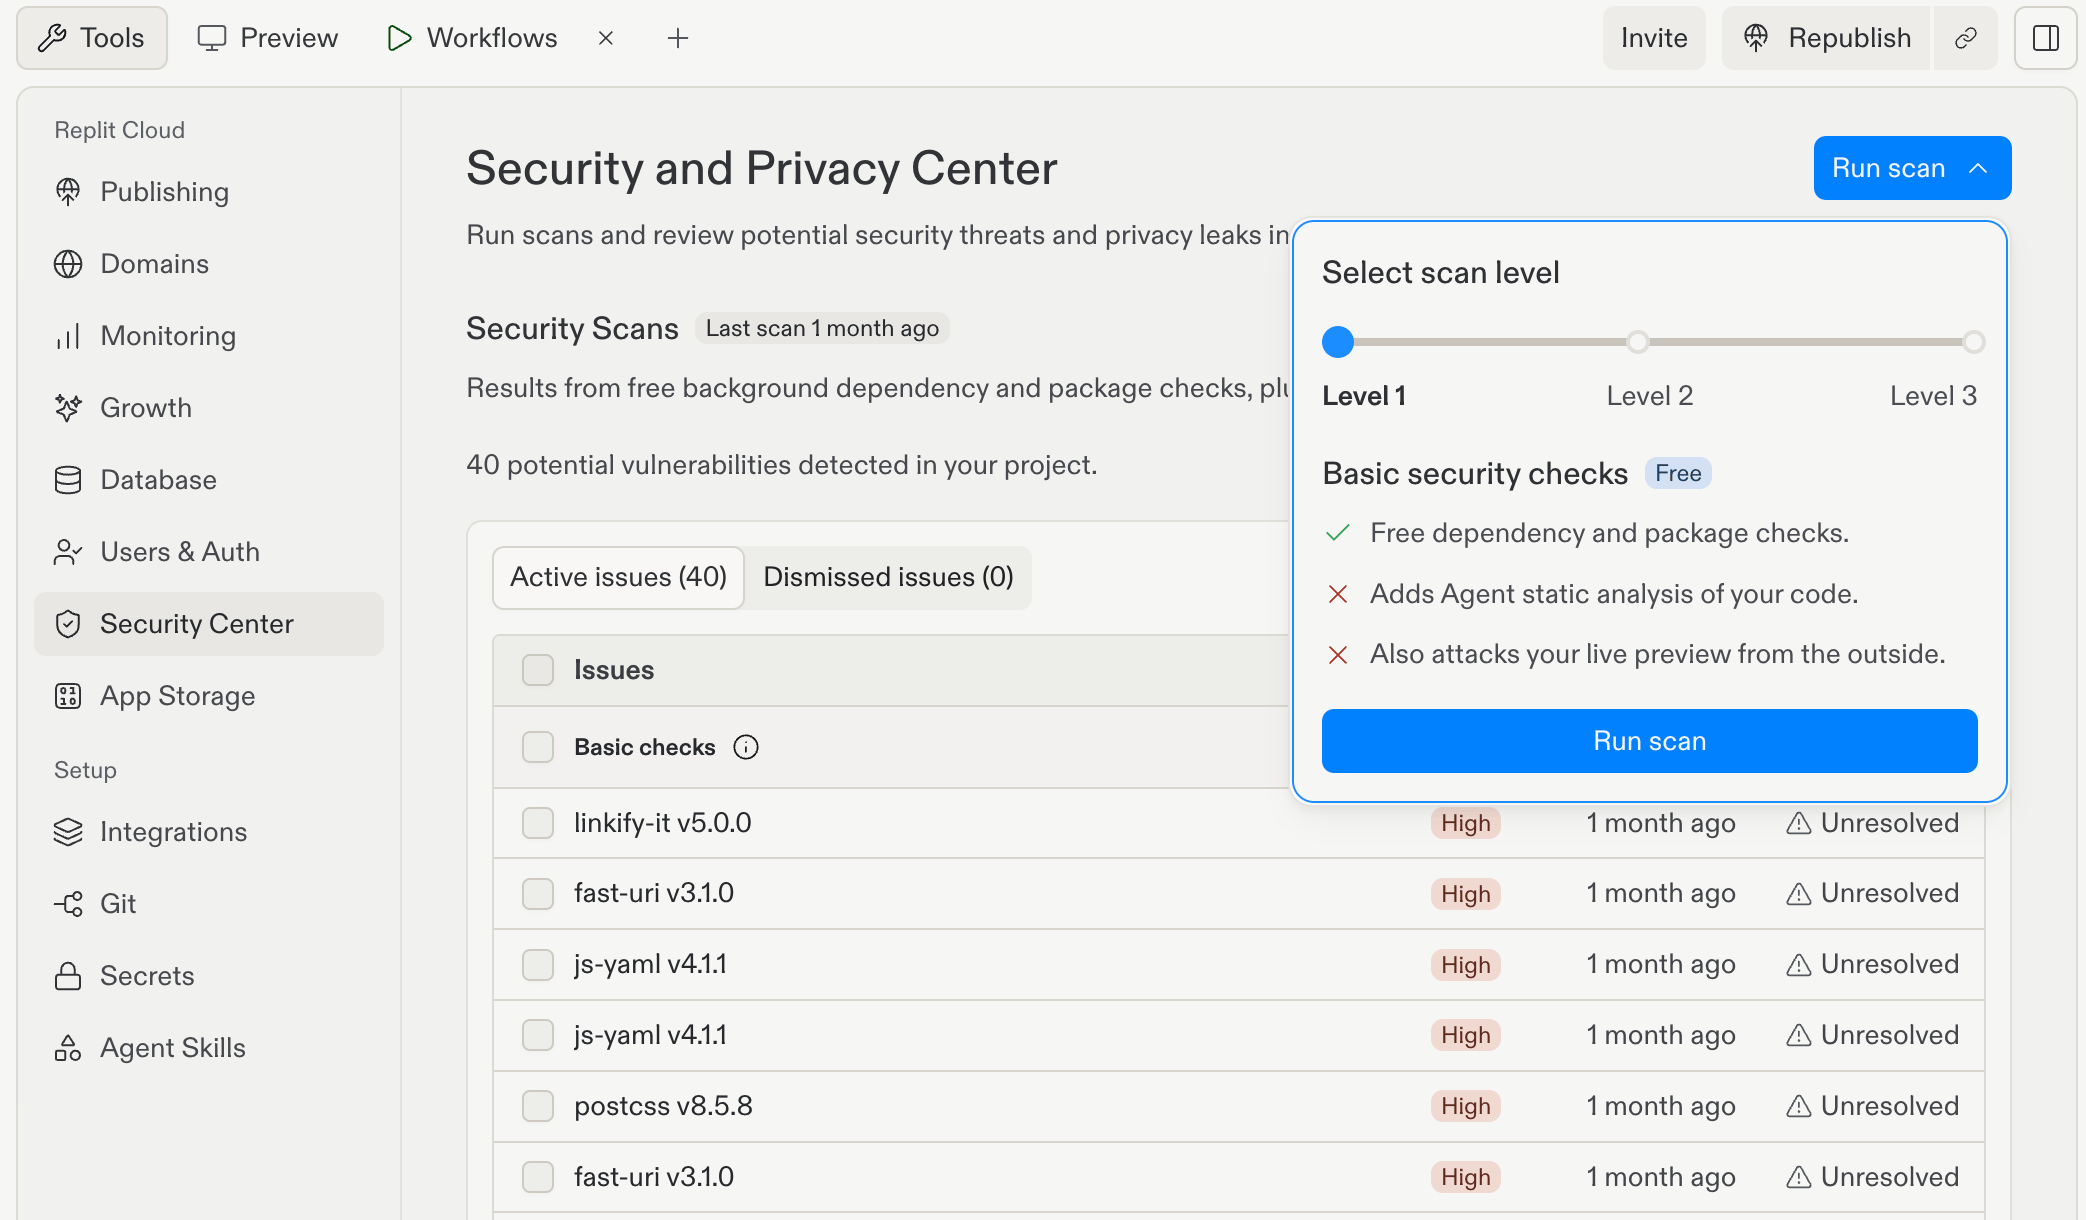
Level 1 includes dependency and package checks. The two crosses show that source-code analysis and live Preview testing are not included.
Level 1 does not run Agent static analysis of your application code or test your live Preview from the outside.
A clean dependency scan does not mean your own code has no vulnerabilities.
Level 2: Deep security scan
Level 2 includes Level 1 checks and adds an Agent security review of your source code. Use it to investigate vulnerabilities in your application’s implementation. Security Agent combines model-based review with static analysis. It can identify risks such as SQL injection, cross-site scripting (XSS), sensitive data in logs, and architectural vulnerabilities. Level 2 does not include an external black-box test of your running app.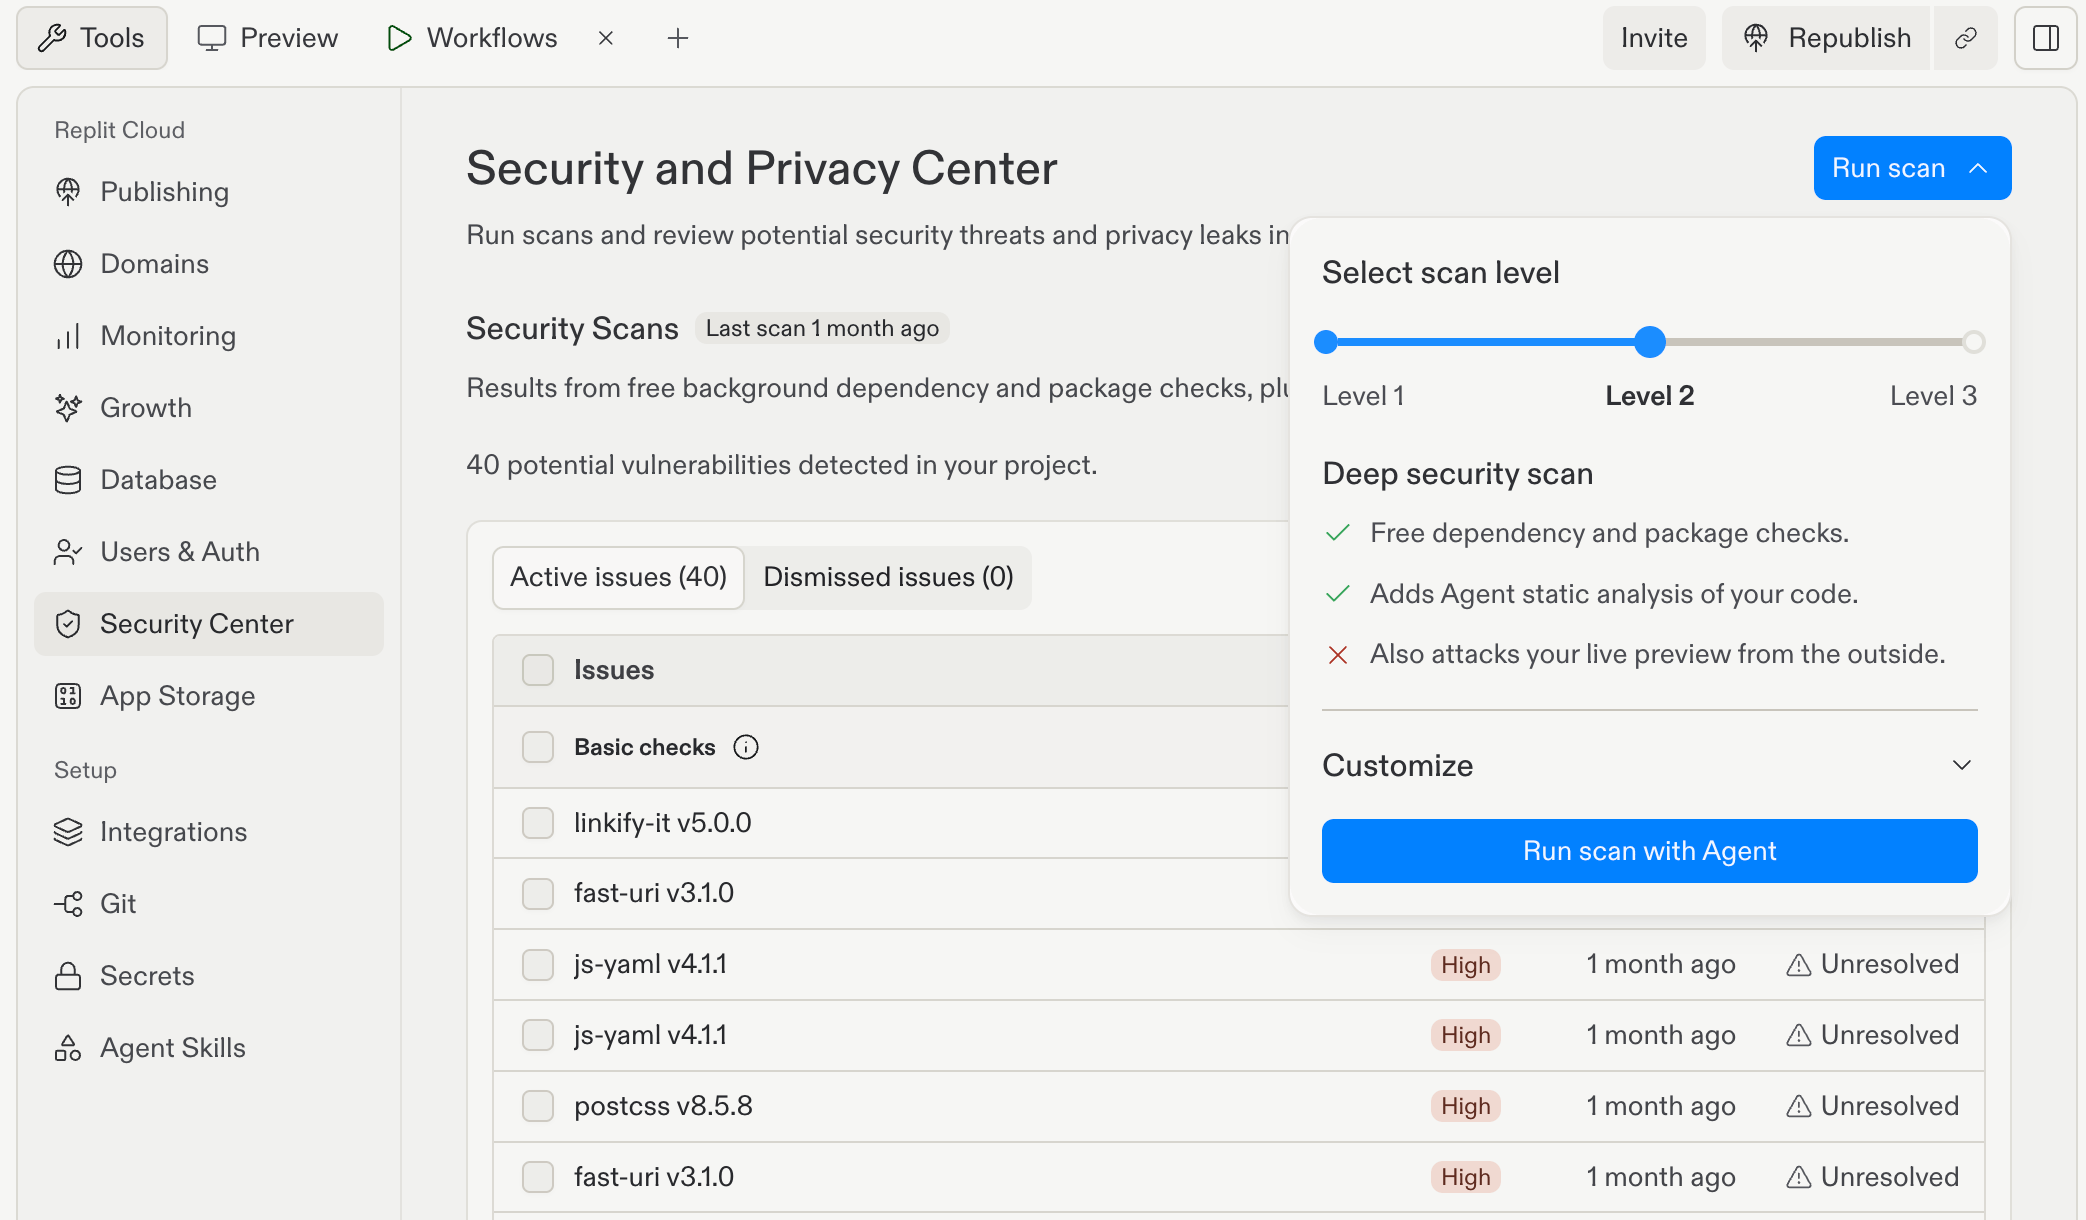
Level 2 adds Agent static analysis. The live Preview test remains excluded, and Customize lets you focus the review.
Level 3: AI pentest
Level 3 includes Level 2 checks and adds an external black-box penetration test of your live Preview. The black-box test examines the running app through browser and network interactions without using its source code. The separate Agent source-code review and black-box test run in parallel. Use Level 3 when you want to examine both the implementation and the running app’s externally observable behavior.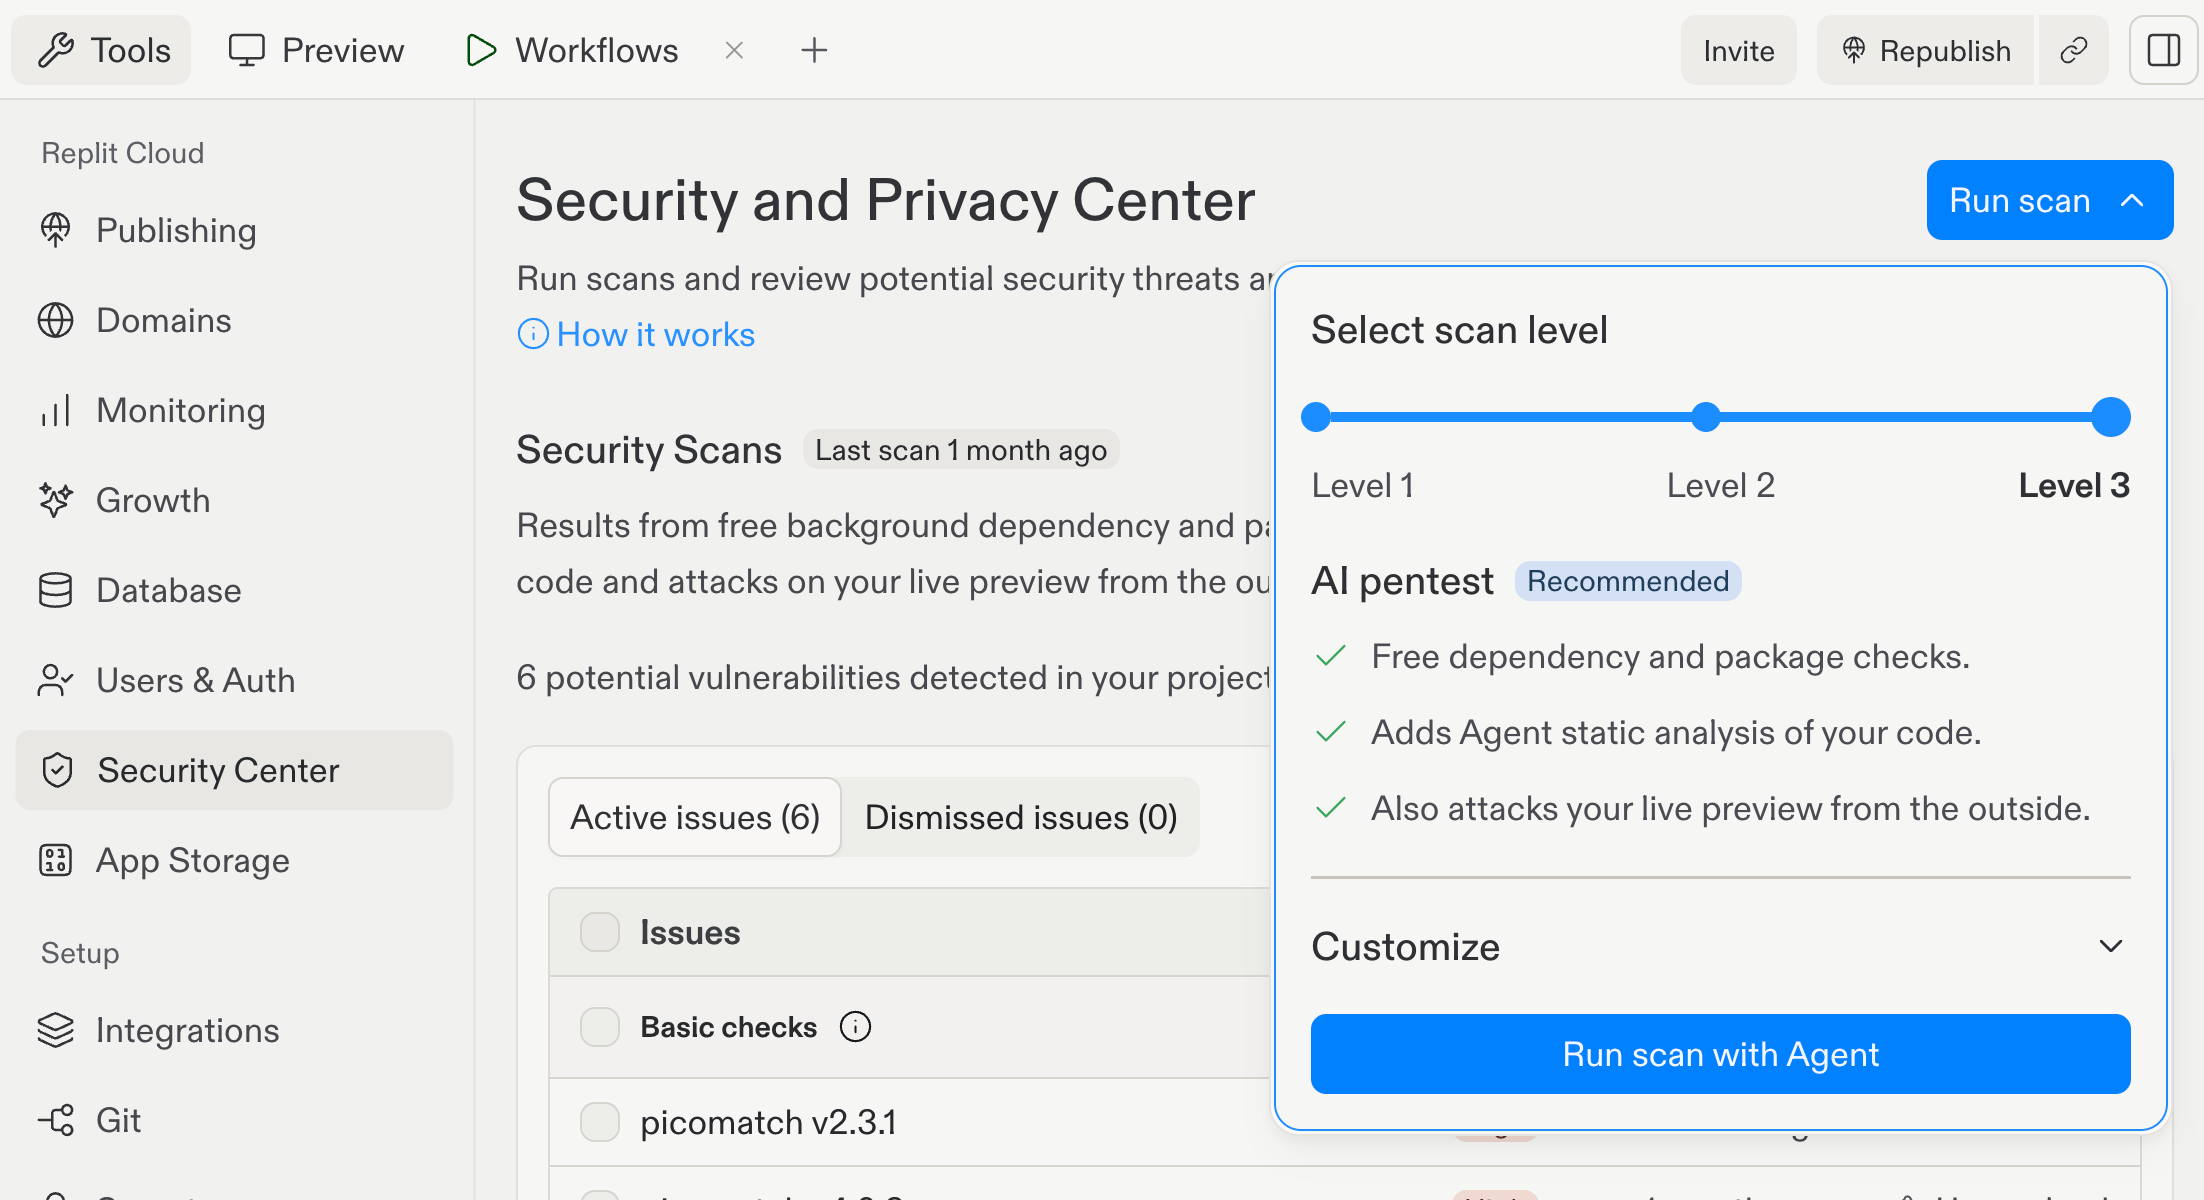
Level 3 enables all three checks: dependencies, Agent source-code analysis, and an external test of the live Preview.
Choose and run a scan
1
Open Security Center
In your project’s Tools pane, select Security Center.
2
Choose a level
Select Run scan at the top of Security Center, then choose the level that matches your review.
3
Run and review
Start the selected scan and wait for it to finish. For Level 3, review findings from both the source-code review and black-box test.
4
Fix and verify
Review findings before sending accepted issues to Agent. After applying fixes, rerun the scan and republish to update your published app.
How levels differ from publish checks
Publish checks are separate from on-demand Security Center scans. Turning on Block publishing of critical vulnerabilities does not run a Level 2 Agent review or a Level 3 black-box test.
Next steps
- Review and manage findings in the Project Security Center.
- Learn the source-code workflow in Agent security scans.
- Test your running app with Black-box pen tests.