

Roles at a glance
Account admin
Billing, seats, security settings, and admin access to every workspace in the account
Workspace admin
Full administrative access to one workspace’s settings and resources, without billing
Member
Can see all other members and create apps and projects
Guest
Can only access and edit apps shared with them
Viewer
Read-only access to apps and deployments
- Built-in roles: Every person in your account has one of these roles, which sets their baseline access
- Custom groups (Enterprise only): Group people by team and grant extra access beyond their role
- App access control: Grant each role, group, or person a specific access level on each app
Usage
Roles
Your Replit account is the billing entity that owns your subscription, seats, and workspaces. Each workspace has its own members and apps. Admin access exists at both levels, while member, guest, and viewer roles apply within a workspace.- Account admins: Manage billing, the subscription, seats, and account-wide security settings such as SAML, SCIM, and audit logs. Every account admin is automatically an admin in every workspace in the account. Manage account admins from the Seats tab in Settings.
- Workspace admins: Have full administrative access to the workspaces they belong to, including members, groups, apps, and workspace settings. They can’t access billing, seats, or other workspaces. In a workspace’s role selector, Admin is the workspace admin role.
- Members: Can create and edit apps and projects and see all other workspace members. They can’t perform administrative actions.
- Guests: Have the lowest access level and can only access and edit apps shared with them. Use this role for external collaborators such as contractors. In workspaces with SAML SSO configured, Guests must use an email outside your SSO domains. Add internal users as members or admins instead.
- Viewers: Have read-only access to apps and deployments, which suits stakeholders who need visibility without editing. Viewers can’t see other viewers in the workspace. See Viewer Seats for details.
Role availability by plan
On Core and Pro, the account admin is the only admin, and you can’t assign a separate workspace admin. On Enterprise, split admin duties between account admins and workspace admins. See Account and Workspace Admins for how to configure each.
On Enterprise, a Guest’s role is locked. You can’t promote a Guest to Member or Admin, or switch them to Viewer, after they’ve been added. Remove the Guest and re-invite them at the role you want. Guests in SCIM-managed workspaces are managed through your identity provider. Enterprise trials don’t have this lock.
If your workspace uses SCIM, you assign roles through synced groups in your identity provider instead of the members page.
Custom groups
Custom groups are available exclusively on the Enterprise plan.
For information on syncing IdP groups to Replit for easier bulk user access management, see SCIM.
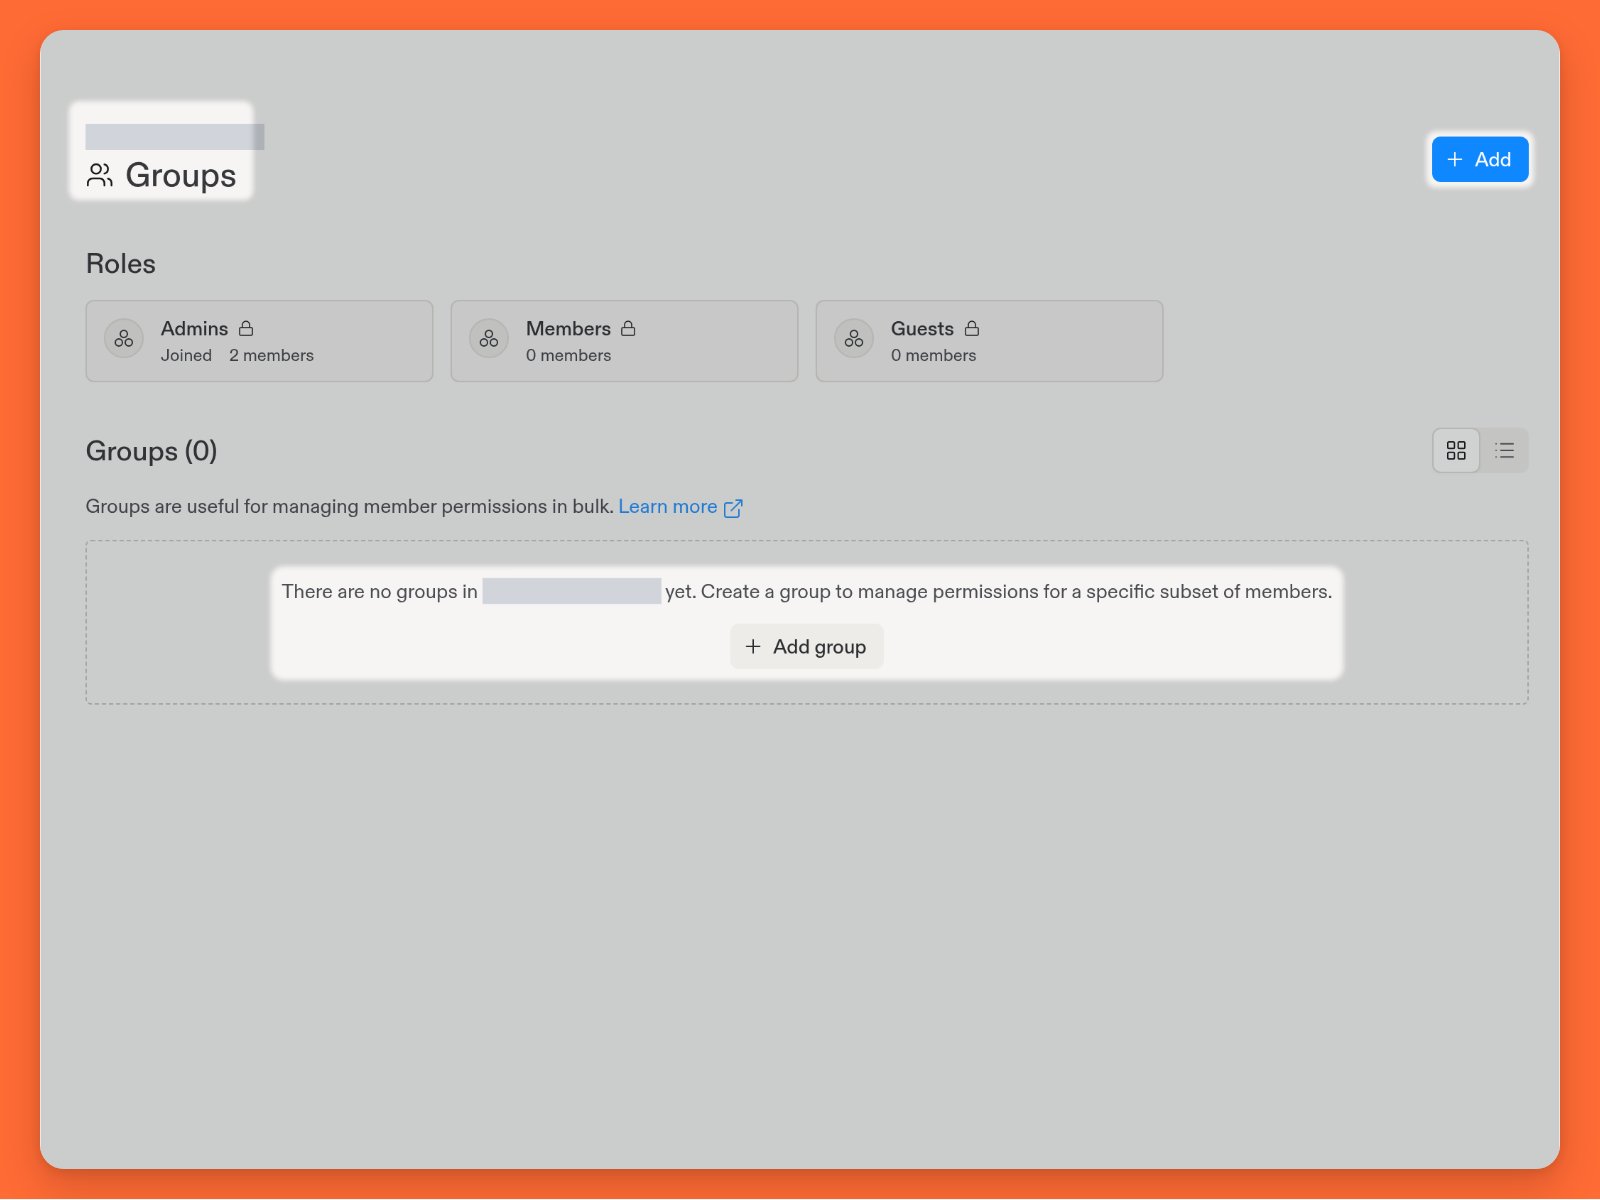
Groups, and select the Groups action. You can also go directly to replit.com/t/<workspace-slug>/groups. Each group card shows its name, color, and member count. Members only see groups to which they have at least viewer access.
This example shows the built-in role cards and a workspace with no custom groups yet.
Creating a group
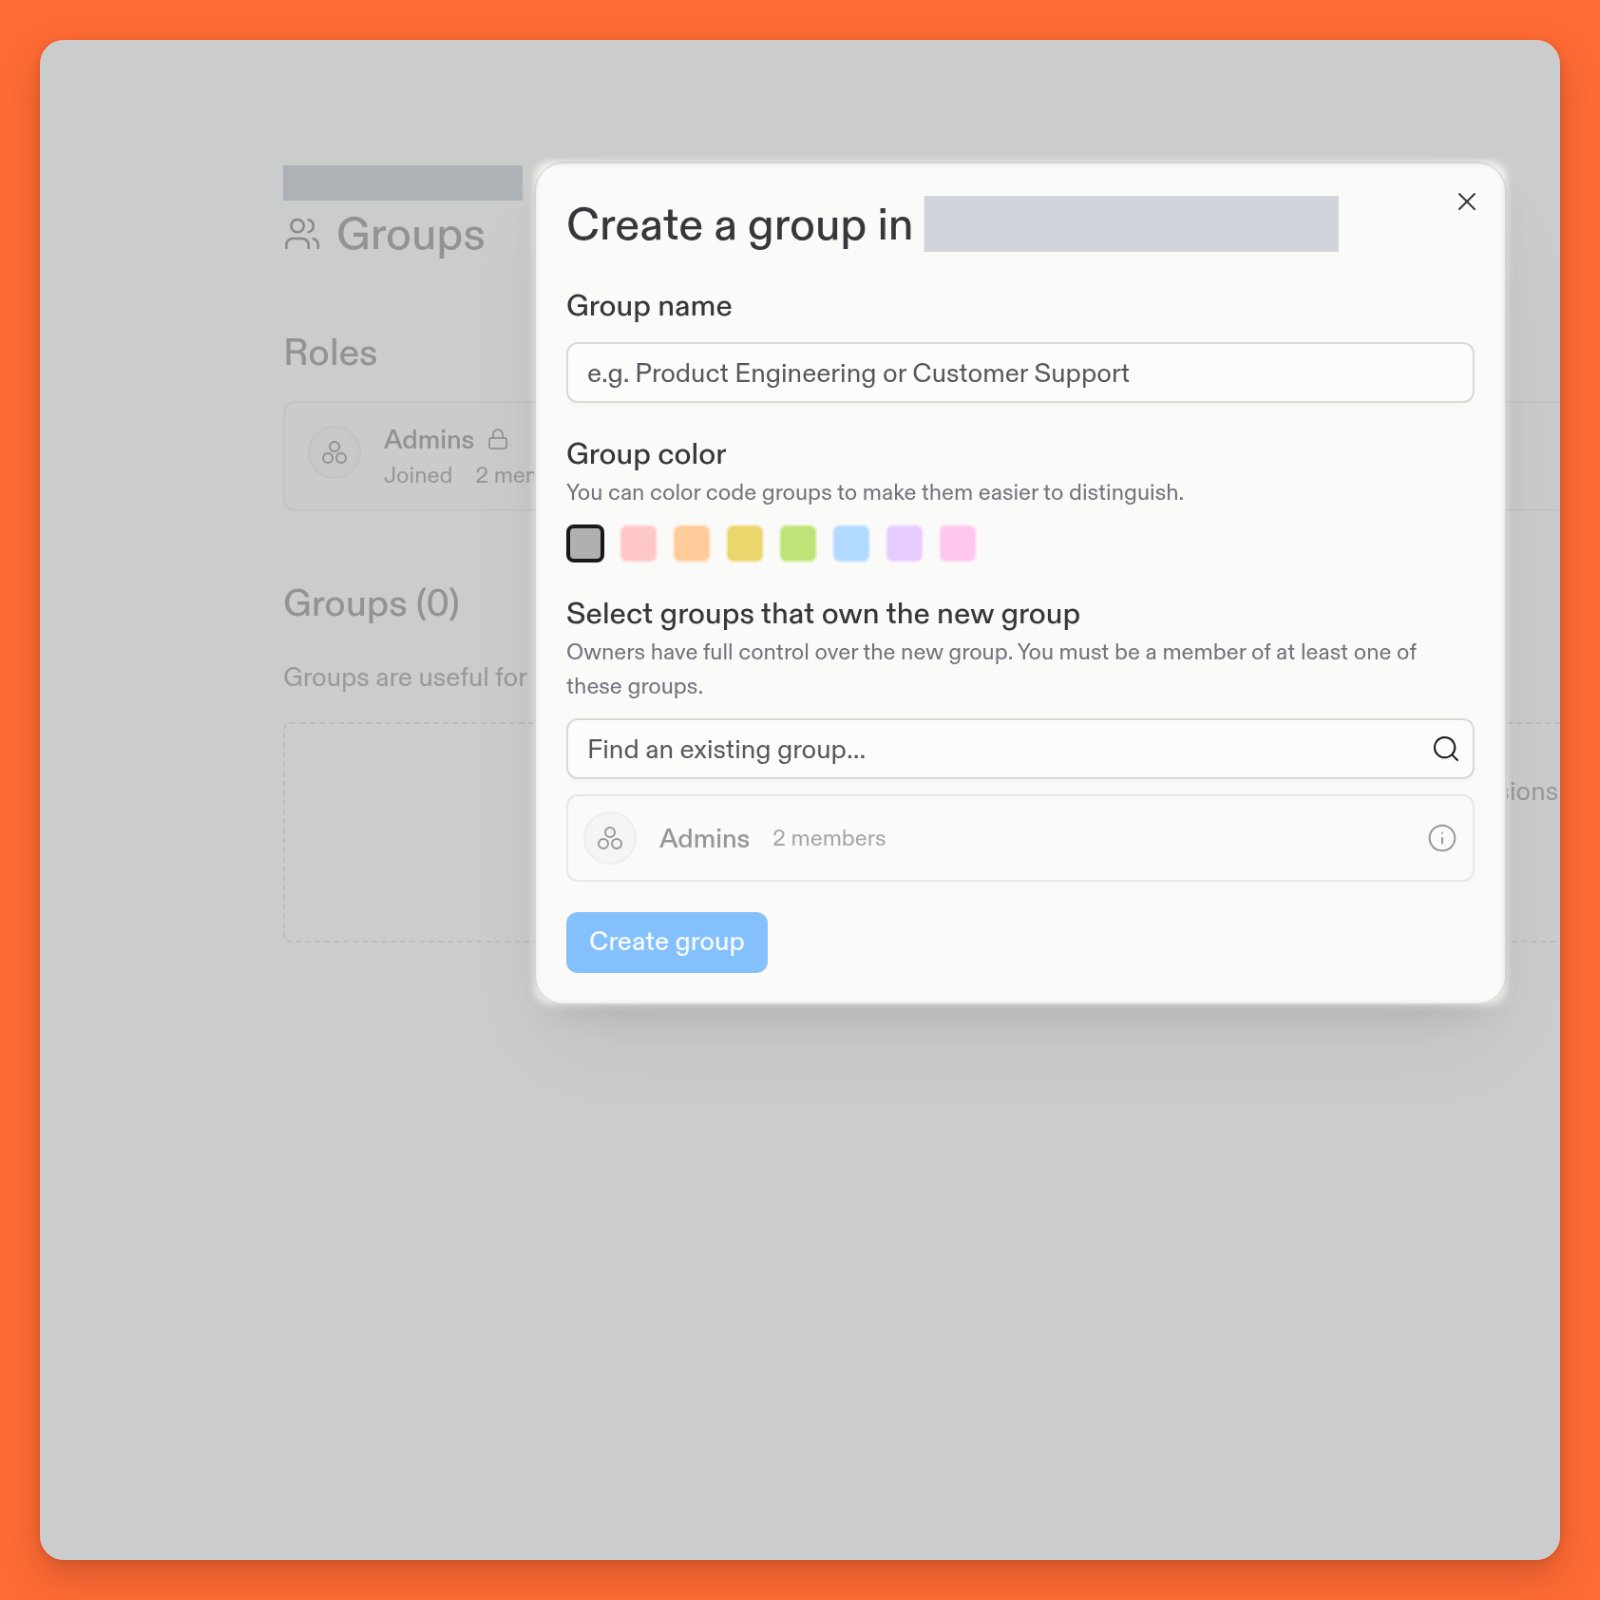
Admins can create custom groups from the Groups page. Select Add in the upper-right corner to open the creation form:- Name your group: Enter a group name
- Choose a color: Distinguish the group visually
- Choose owner groups: You must belong to at least one group that owns the new group. In this example, Admins is already listed as an owner
Managing groups
Select any group card to access its management interface. Group management includes member addition, removal, and permissions configuration. Adding members to groups: To add a member to a group, select Add in the upper-right corner. This action becomes disabled if the person you’re adding is not part of the workspace and there are insufficient seats available. You can search for new members by username or email. If the new member is not part of the workspace, a warning appears to confirm the action. After adding the new member, they appear in the group member list. They immediately gain access to Replit Apps and other resources available to the group. Removing members from groups: To remove a group member, select the trash icon on the right side of the member row. You can also open the actions menu using the three-dot button and select Remove from group. This opens a confirmation modal. When removing members from custom groups, they retain their base role access but lose their group-specific access.Setting group permissions
Assign a workspace permission level to a group to define what its members can do across the workspace. Select the group, choose Permissions in the left navigation, and open the Workspace tab. The permission levels are:- Owner: Can perform all workspace actions, including deleting the workspace
- Billing manager: Can update the workspace’s payment information, add and remove seats, and set spending limits
- Manager: Can create and manage groups, add and remove workspace members, and view billing information
- Editor: Can create new apps and view usage information
- Viewer: Can see basic information about the workspace
Owner is reserved for admins. You can’t grant it to a custom group.
These workspace permissions are separate from app access, which you manage on each app. To see which apps a group can access, select the group, choose Permissions, and open the Apps tab.
App access control
Control who can access and collaborate on your apps using Replit’s Access feature. Assign access to roles and groups to share specific apps with the right members while maintaining security across your workspace.Setting app access
How to manage app access
How to manage app access
From any app, select Invite in the upper right corner (to the left of Publish) to open the Access panel.
- Roles: Rows such as Admins in your workspace, Members in your workspace, Guests in your workspace, and Viewers in your workspace show the access each role has
- Custom groups and people: Search to find and grant app access to specific custom groups or individual members
Access levels
You can assign different access levels to each role and group for fine-grained control:- Owner: Full permissions, including deleting the app
- Publisher: Can edit and publish the app
- Editor: Can edit the app, but can’t publish it
- Read-only: Can view the published app, but can’t open its workspace
- None: No access to the app